Security Notice: Important Update Regarding Recent Global PHP Flaw
On 21 October 2026, global cybersecurity teams identified a significant security flaw affecting PHP, a foundational technology used across the internet to power dynamic websites and online applications.
We want to reassure all our customers immediately: all websites hosted on our servers were fully updated and secured by 11:52 PM last night. You do not need to take any action.
What is PHP?
Think of a website like a store. The design and text you see on screen are like the window display. PHP is the behind-the-scenes engine or staff member that processes your order, fetches items from the stockroom (database), and hands them back to you dynamically on the page.
Because millions of websites rely on PHP to run, updates to this engine are essential to keep websites running safely and smoothly.
What Is the Security Risk?
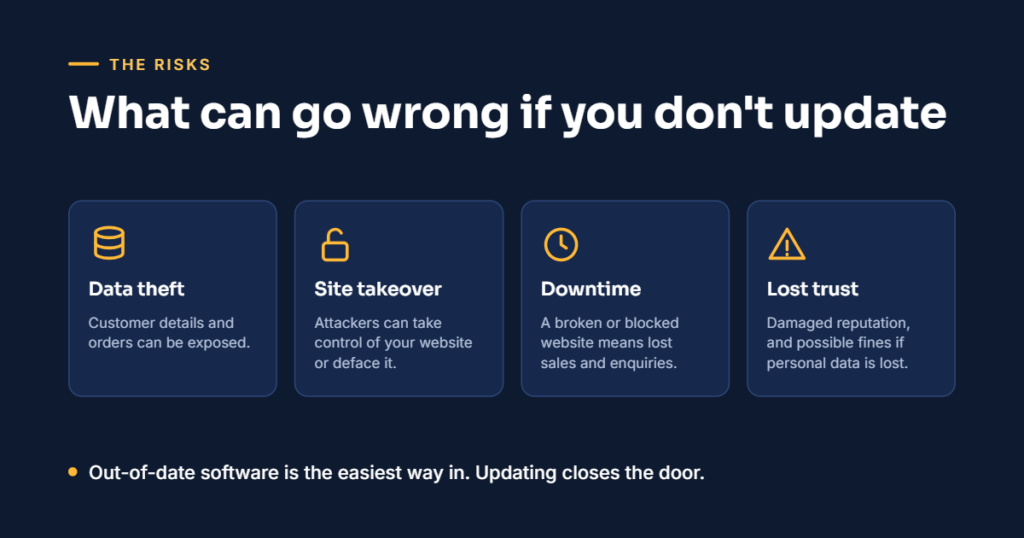
Security researchers discovered a flaw in how the PHP engine handles sudden errors or memory spikes. In layperson’s terms: under very specific conditions, an attacker could send a specially crafted request to trick the server while it was busy handling an error. This could allow unauthorized access to run malicious commands or tamper with server files.
As soon as official fixes were made available by security maintainers, hosting providers worldwide began rolling out patches, including us!
What Actions Do You Need to Take?
If Your Website is Hosted With Us:
No action is required.
Our technical team monitored the release, tested the official fix, and patched every server across our network by 11:52 PM last night. Your website is completely protected, and all systems are operating normally.
If Your Website is Hosted or Managed by Others:
If you run or manage other websites outside of our network, we recommend contacting your hosting provider or web developer to ensure they have applied the latest PHP security patch to those environments as well. Updating WordPress and its Plugins won’t fix this problem, as the flaw is in the software that makes WordPress work.
If your website is not able to support the updated software there are other ways to protect against this treat. They require the websites to be placed behind ‘logical firewalls’ to provide an element or protection against this attack, but this should be undertaken by a professional as it may require migrating domains and changing some very critical settings.
Questions or Concerns?
Your security and peace of mind are our highest priorities. If you have any further questions or would like to speak with us about how we can help you regarding this PHP security flaw, or any other IT related concerns, please get in touch via the details below and we ill be happy to have a chat with you.
For Further Information or advice, please contact the Magikos IT Team or fill in the form below and we will contact you.
Tel: 01344 204019
Email: [email protected]